Gartner’s How to Achieve the Minimum Viable AI Governance


Most privilege escalation traces to privilege management rather than a patchable flaw. These articles cover Active Directory and Entra ID configuration weaknesses – NTLM, cached credentials, pass-the-hash, delegation, legacy permissions – and the specific settings that stop lateral movement before it starts.
From patches and configuration changes to software removal, the devil is in the details when it comes to remediating endpoints. Here we look at the role played by impact analysis, controlled execution, verification, and rollback in preventing operation disruption.
Topic
Author
Most cyber risk isn’t unknown, it’s unresolved. Identity drift, exposed remote access, and shadow AI keep known exposures alive. Here's how continuous risk reduction can close the gap.

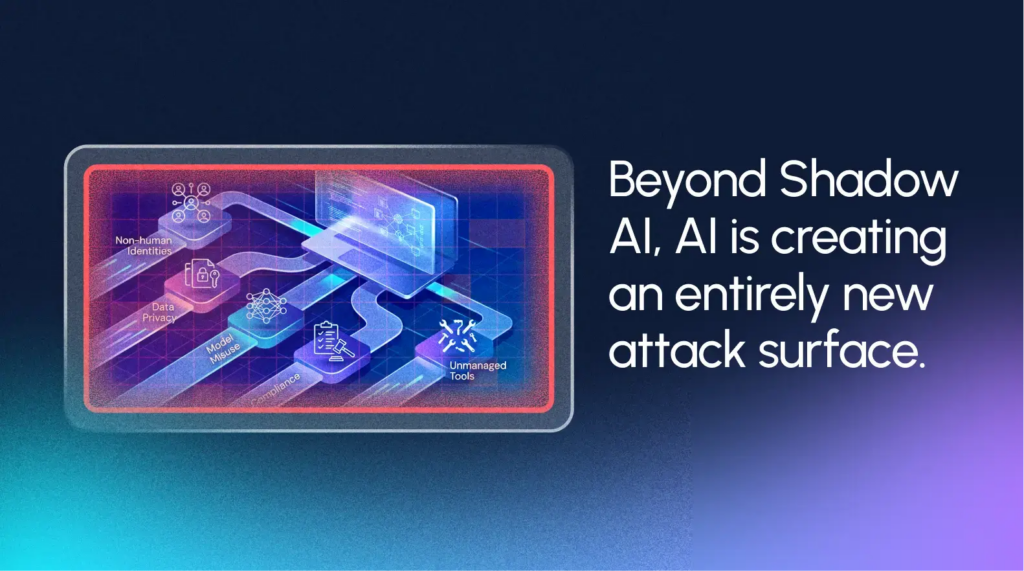
AI has introduced new applications, identities, permissions, and data flows. Explore five ways it is expanding the enterprise attack surface and increasing risk.
Capture the noteworthy, cut the noise!
Get Remedio’s monthly endpoint security briefing on emerging risks, hardening strategies, and what’s new in enterprise security.
Subscribe to our newsletter to stay up-to-date and in the loop.
One email a month. Unsubscribe anytime.

Plaintext passwords and weak configurations continue to expose organizations to supply chain attacks. Learn how to eliminate these preventable security risks.

Least privilege depends on more than permissions alone. Learn how secure configurations help enforce access controls while reducing operational complexity.


Active Directory remains one of the most targeted enterprise assets. Learn how stronger configurations and continuous oversight help protect your identity infrastructure.

Remote Desktop Protocol remains a favorite target for attackers. Learn how to reduce RDP exposure through stronger configurations, hardening, and access controls.

LockBit 2.0 doesn't succeed because organizations lack security tools. It succeeds when the last mile of hardening is left open. Learn how the ransomware operates and the practical counter-measures that close its favorite entry points.


Some of the riskiest Windows exposures aren't new threats at all. They're legacy settings that survived every upgrade. This post explains how to find and fix them safely.


Managing Active Directory threats means more than spotting misconfigurations. Learn where AD exposure builds, how posture degrades over time, and how to close the gap with safe remediation.

NTLM still shows up in cloud-first environments more often than security teams would like, and that’s the problem. This legacy authentication protocol keeps extending the exposure gap between what you’ve modernized and what adversaries can still exploit. In this article, we break down why NTLM remains a stubborn source of risk, where it hides in real enterprise environments, and what operators can do to phase it out without creating operational chaos.