Gartner’s How to Achieve the Minimum Viable AI Governance


Patching is necessary and insufficient: a large share of exploitable exposure has no patch at all, only a configuration fix. These articles cover prioritizing what to patch first, cutting time-to-deploy, working around reboot and downtime constraints, and recognizing where patching stops helping.
Dario Amodei just made the most consequential call yet for slowing AI down. Buried in it were security concerns every CISO should know. The exploits weren't new: unauthenticated service, leaked tokens, unsafe file parsing, secrets on a production worker.
Topic
Author
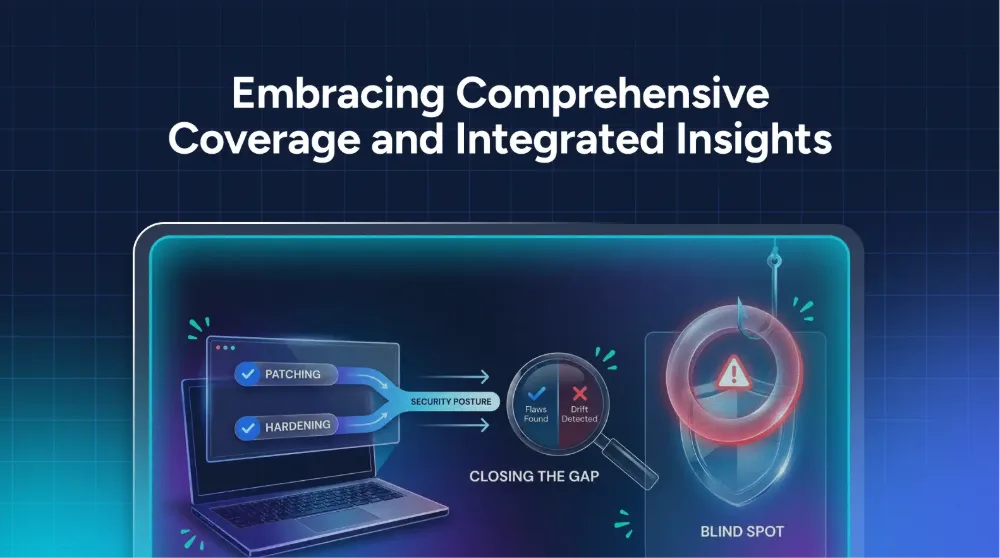
Separating vulnerability patching from configuration hardening creates a widening exposure gap and severe operational drag. Learn how borrowing principles from DevOps allows security teams to unify exposure intelligence and enforce continuous, safe remediation.

Autonomous Endpoint Management helps organizations maintain secure configurations, reduce operational burden, and continuously protect dynamic endpoint environments.

Capture the noteworthy, cut the noise!
Get Remedio’s monthly endpoint security briefing on emerging risks, hardening strategies, and what’s new in enterprise security.
Subscribe to our newsletter to stay up-to-date and in the loop.
One email a month. Unsubscribe anytime.

Strong cyber hygiene reduces risk long before an attack occurs. Learn the practices that help organizations maintain secure, resilient, and well-managed environments.

Operating systems are still a key part of your attack surface. This post explains why your patching cycle should account for them more directly.

Linux has a reputation for being secure, but reputation doesn’t harden endpoints. As Linux adoption grows across servers, cloud environments, and embedded systems, misconfigurations create real exposure that adversaries are happy to exploit. This article looks at where Linux security breaks down in practice and how teams can reduce that exposure with continuous visibility and safe remediation.