Gartner’s How to Achieve the Minimum Viable AI Governance


Tune in to tune up your endpoint defenses!
Your go-to destination for all things posture management & configuration security…
A single 32-bit multiplication is enough to turn a malicious PDF into memory corruption. We break down the integer overflow vulnerability behind CVE-2026-81983 and show exactly where Acrobat’s safety check fails.
Topic
Author
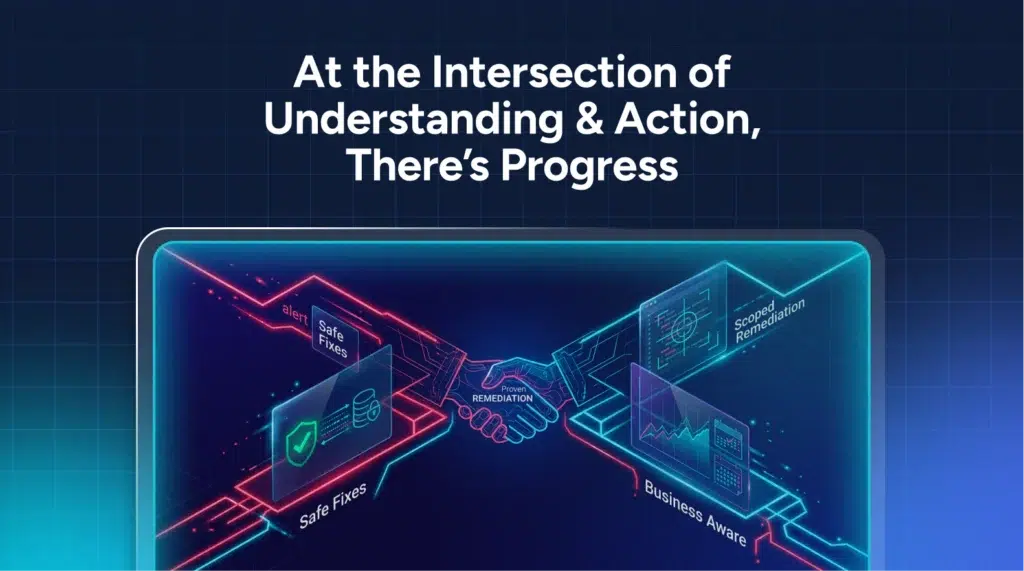
The next battleground isn’t speed alone, but an embrace of business-aware control that allow operators to reduce exposure decisively, safely, and at scale through autonomous remediation.

Learn how clear IT governance policies and repeatable processes systematically reduce decision fatigue, simplify change management, and lower security risk.

Capture the noteworthy, cut the noise!
Get Remedio’s monthly endpoint security briefing on emerging risks, hardening strategies, and what’s new in enterprise security.
Subscribe to our newsletter to stay up-to-date and in the loop.
One email a month. Unsubscribe anytime.
EDR tells you what happened. Configuration security tells you why it was possible. Learn how integrating both helps teams reduce exposure, prioritize faster, and drive safe remediation.
Personal devices create management blind spots while borrowed trust and AI-enabled access expand the attack surface. Here's what operators can do to reduce exposure...
Most cyber risk isn’t unknown, it’s unresolved. Identity drift, exposed remote access, and shadow AI keep known exposures alive. Here's how continuous risk reduction can close the gap.
Most security teams already know misconfigurations matter. The real issue is that they rarely behave like isolated mistakes. They accumulate across endpoints, identities, cloud services, and network devices until the environment becomes harder to trust, harder to operate, and harder to defend.
Fragmented enforcement, protracted workflows, complicated change management, and unknown impact slow down your business. Safe, dependency-aware remediation are essential to reducing exposure without disrupting the business.
Cyber exposure isn’t just a security problem, it’s a financial one. Remediation delays and misconfigurations increase the exposure gap and add to business risk. Reducing time to safe remediation is essential for stronger cyber posture and lower operational drag.
For years, detection stacks grew, triage workflows expanded, ticket queues became normal, and patch windows stretched. Today, finding vulnerabilities is no longer the hard part. Safe remediation is.
This article explains how configuration debt increases breach risk, weakens compliance, and creates operational drag. It also explains why continuous, safe remediation is the only reliable way to pay it down, and provides some guidance or so doing.

Security teams don’t struggle because they miss endpoint risks. They struggle because the same exposures keep coming back. Here we explain where and why risk management breaks down and what can be done to prevent risk recurrence.